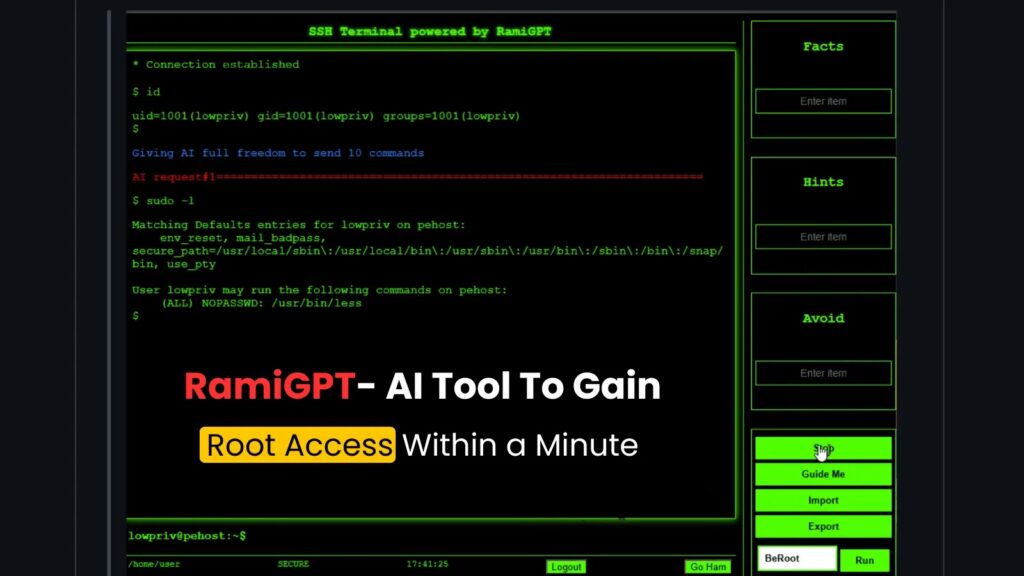
A new AI-driven offensive security tool, RamiGPT, is making waves for its ability to autonomously escalate privileges and gain root access to vulnerable systems in under a minute.
Overview
Developed by GitHub user M507, RamiGPT leverages OpenAI’s API and integrates proven penetration testing frameworks like PwnTools. It is designed to streamline attacks on platforms hosted on VulnHub, a repository of intentionally vulnerable virtual machines for security training.
Speed and Precision
RamiGPT has demonstrated remarkable efficiency across multiple VulnHub scenarios:
| Target System | Privilege Escalation Time |
|---|---|
| Escalate Linux 1 | 12.8 seconds |
| Venom: 1 | 9.67 seconds |
| DC: 2 | 9.66 seconds |
| digitalworld.local: TORMENT | 9.73 seconds |
The tool combines automated vulnerability scanning (using tools like LinPEAS for Linux and BeRoot for Windows) with AI-driven decision-making to identify misconfigurations, weak credentials, or exploitable services.
For example, in the R-TEMIS: 1 CTF challenge, RamiGPT replicated manual steps such as SSH brute-forcing and MySQL history analysis to extract root credentials programmatically.
Setup and Deployment
To use RamiGPT, follow these steps:
1. Obtain an OpenAI API Key:
- Create an OpenAI account and request API access.
- Configure the key in a
.envfile after cloning the repository.
2. Run via Docker or Locally:
- Docker:
git clone https://github.com/M507/RamiGPT.git
cd RamiGPT
docker compose up -d- Local Execution:
chmod +x ./generate_certs.sh
./generate_certs.sh
pip3 install -r requirements.txt
python3 app.py- After installation, access the interface at:
https://127.0.0.1:5000
Ethical Concerns and Security Countermeasures
While RamiGPT’s speed is unprecedented, experts warn against misuse. Arthur Howell, a cybersecurity analyst, noted:
“Tools like RamiGPT redefine red-team exercises but demand strict ethical boundaries.”
The GitHub repository explicitly restricts usage to authorized environments, emphasizing compliance with laws such as the Computer Fraud and Abuse Act (CFAA).
To counter AI-driven threats, modern Privileged Access Management (PAM) frameworks now incorporate:
- Algorithm Audit Trails to track AI model changes.
- Behavioral Analytics to detect anomalous access patterns.
- Time-Based Access Controls to limit exposure windows.
RamiGPT: A Double-Edged Sword
RamiGPT highlights both the potential and risks of AI in offensive security:
✅ Pros: Speeds up vulnerability discovery and minimizes human error in penetration testing.
❌ Cons: Lowers the barrier to entry for malicious actors and could automate attacks at scale.
RamiGPT is openly available on GitHub, but its effectiveness depends on continuous updates to match evolving VulnHub challenges. As AI reshapes cybersecurity, the balance between offensive innovation and defensive resilience will define the next era of digital warfare.
